Start here
What Is an AI Audit Copilot? Uses, Limits, and Evaluation
Learn what an AI audit copilot does, where human review matters, and how to evaluate evidence references, control testing, and workpaper quality.
Read the guide
Get the latest on security trends, compliance frameworks, and IABuddy news.
Start here
Learn what an AI audit copilot does, where human review matters, and how to evaluate evidence references, control testing, and workpaper quality.
Read the guide
Compliance
Use risk-based scoping, precise review controls, reliable information, issue evaluation, and timely remediation to address SOX gaps without promising prevention.
Compliance
Identify key SOX controls through risk coverage, relevant assertions, precision, and dependencies rather than assuming every automated or high-level control is key.
Compliance
Plan IPE testing around report purpose, source logic, parameters, completeness, accuracy, precision, and change handling without mistaking file integrity for proof.
Compliance
Design multi-client audit workflows with clear workspaces, least-privilege access, isolated retrieval, controlled sharing, and tested offboarding practices.
Compliance
Connect the audit plan to strategic objectives and risks, preserve independence, and report decision-useful findings without becoming the owner of management's controls.
Audit Technology
See where AI can assist SOX testing, from evidence intake to workpapers, and measure complete preparation and review effort rather than unverified speed claims.
Audit Technology
Compare rules-based automation and AI for audit tasks, including structured data, document interpretation, validation, exception handling, and human review.
Audit Technology
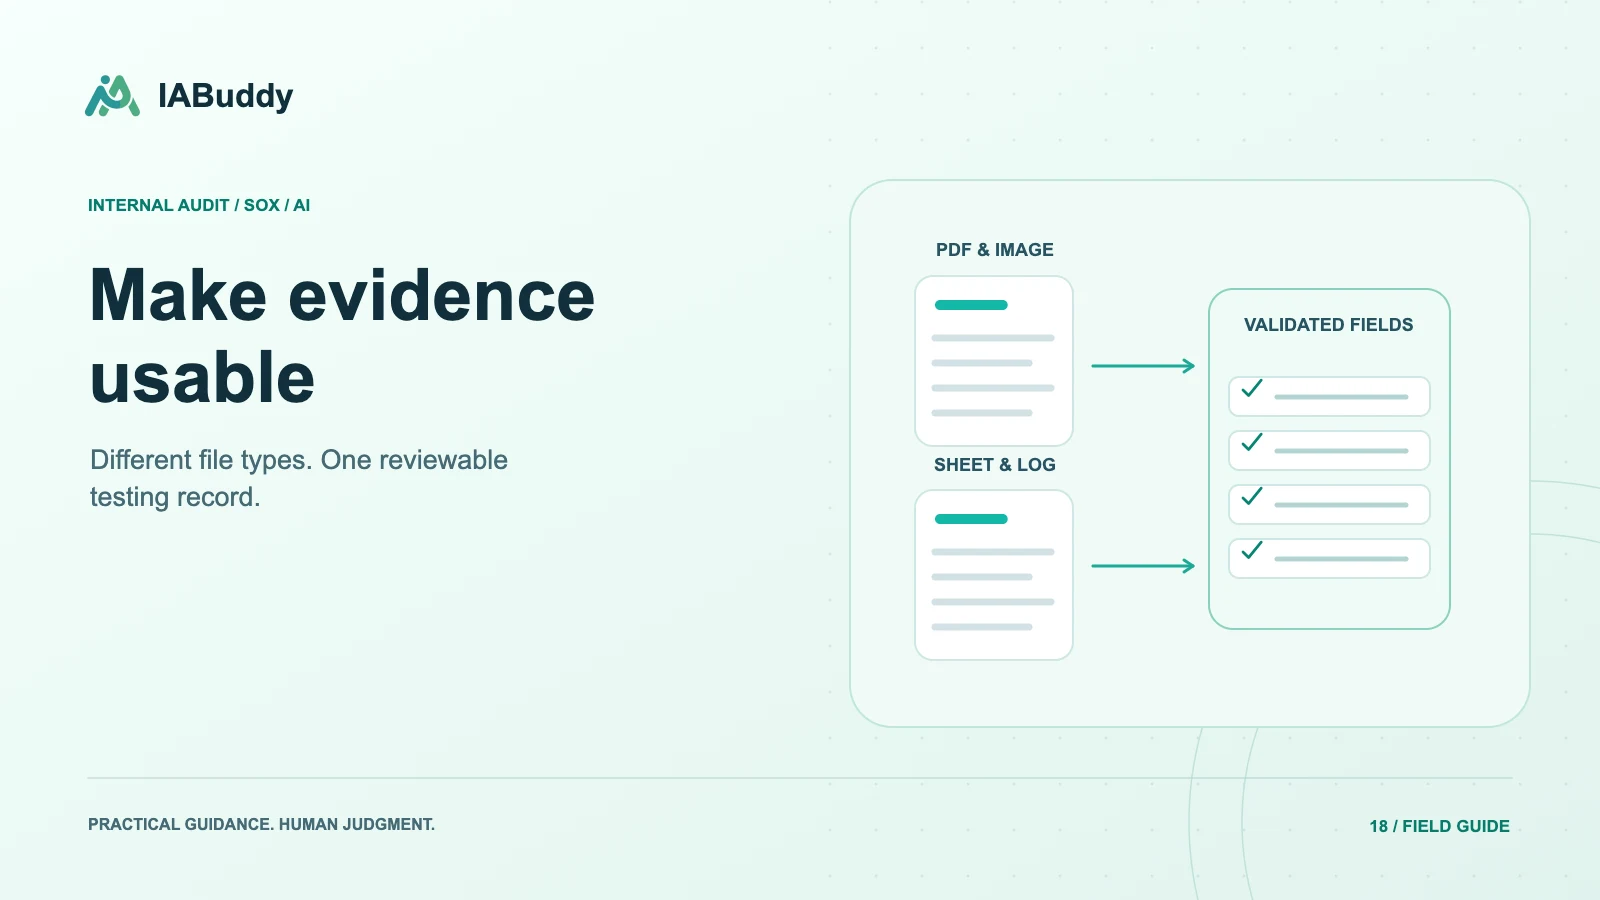
Understand document parsing, OCR, AI extraction, source references, and validation for PDFs, spreadsheets, screenshots, and logs used in audit testing.
Compliance
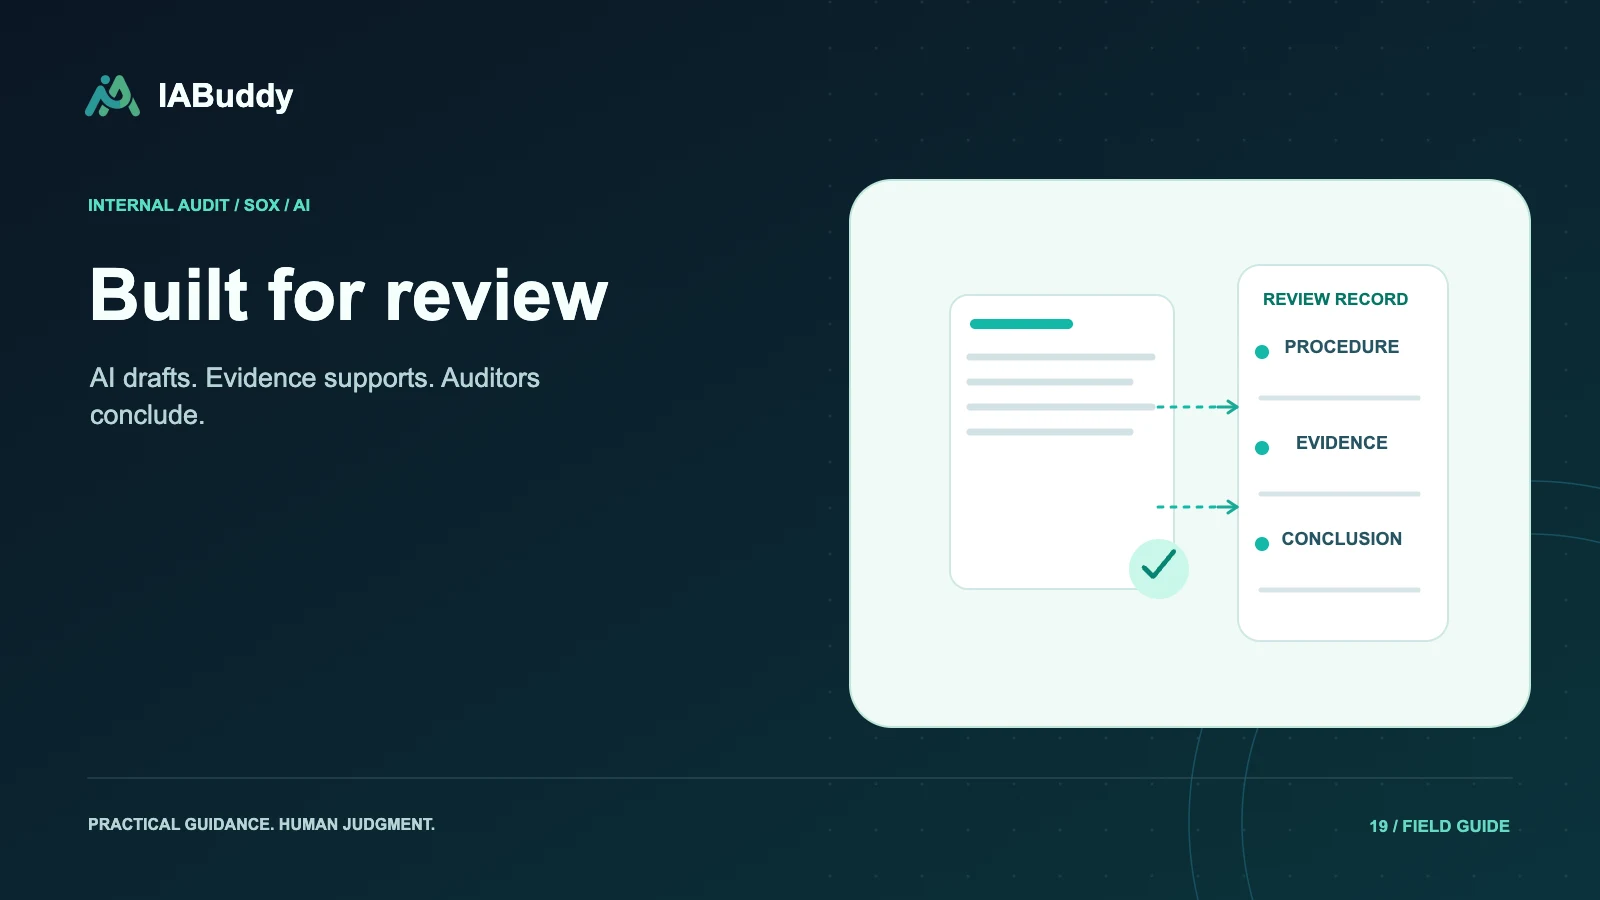
Learn how AI can assist workpaper drafting, what AS 1215 documentation should support, and why software output does not guarantee external auditor reliance.
Security
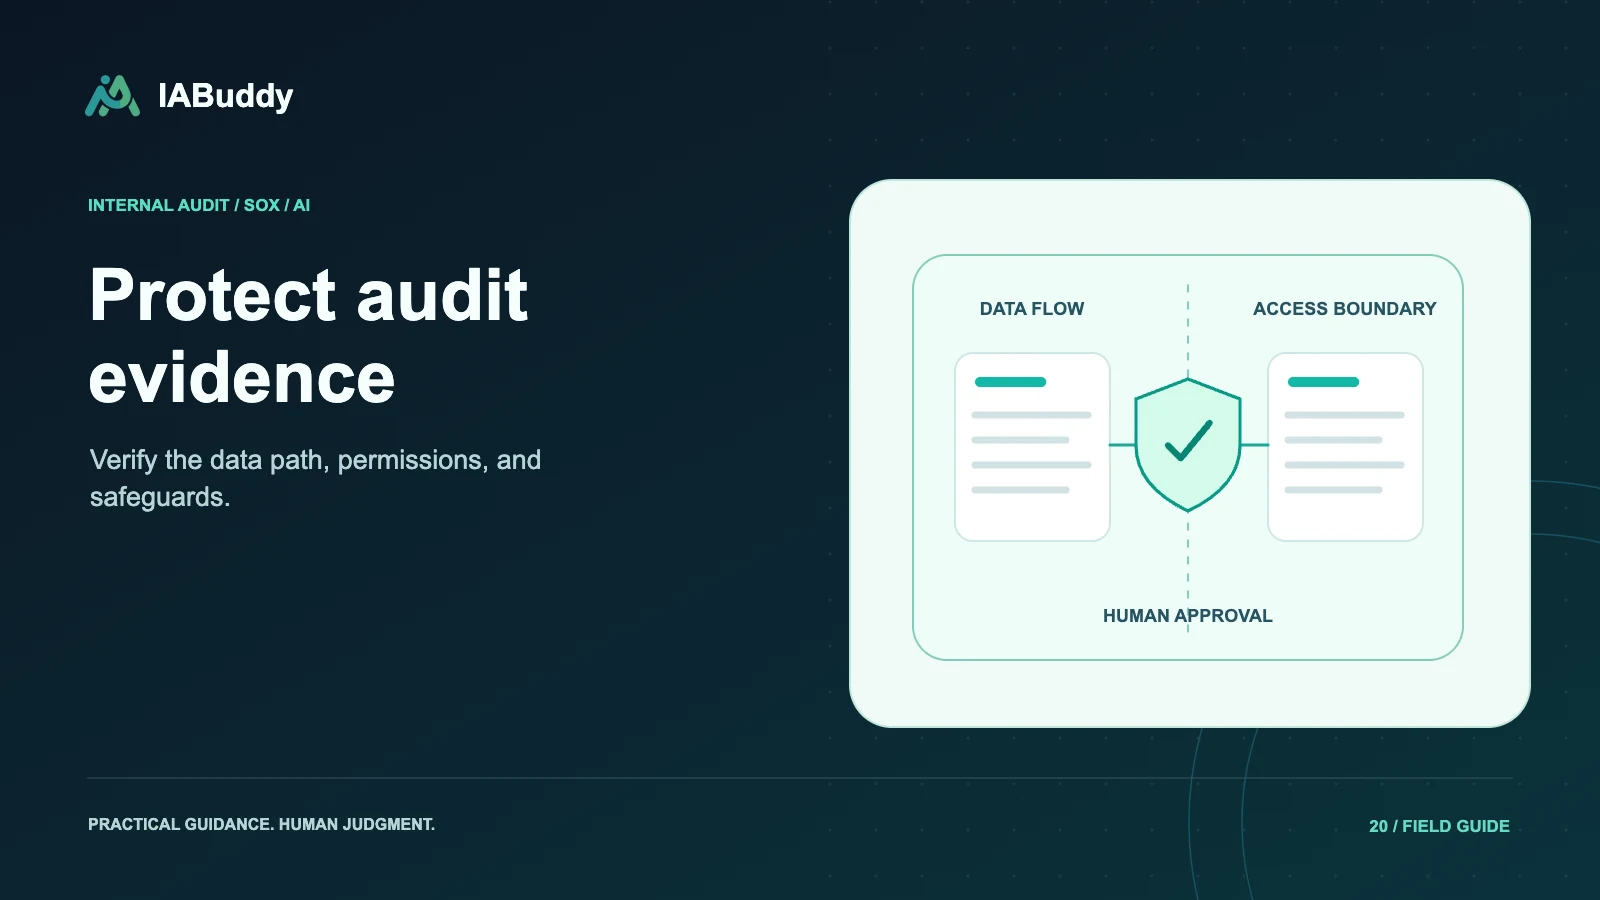
Assess prompt injection, data exposure, access boundaries, subprocessors, retention, model training, and human approval before using AI with audit evidence.
Compliance
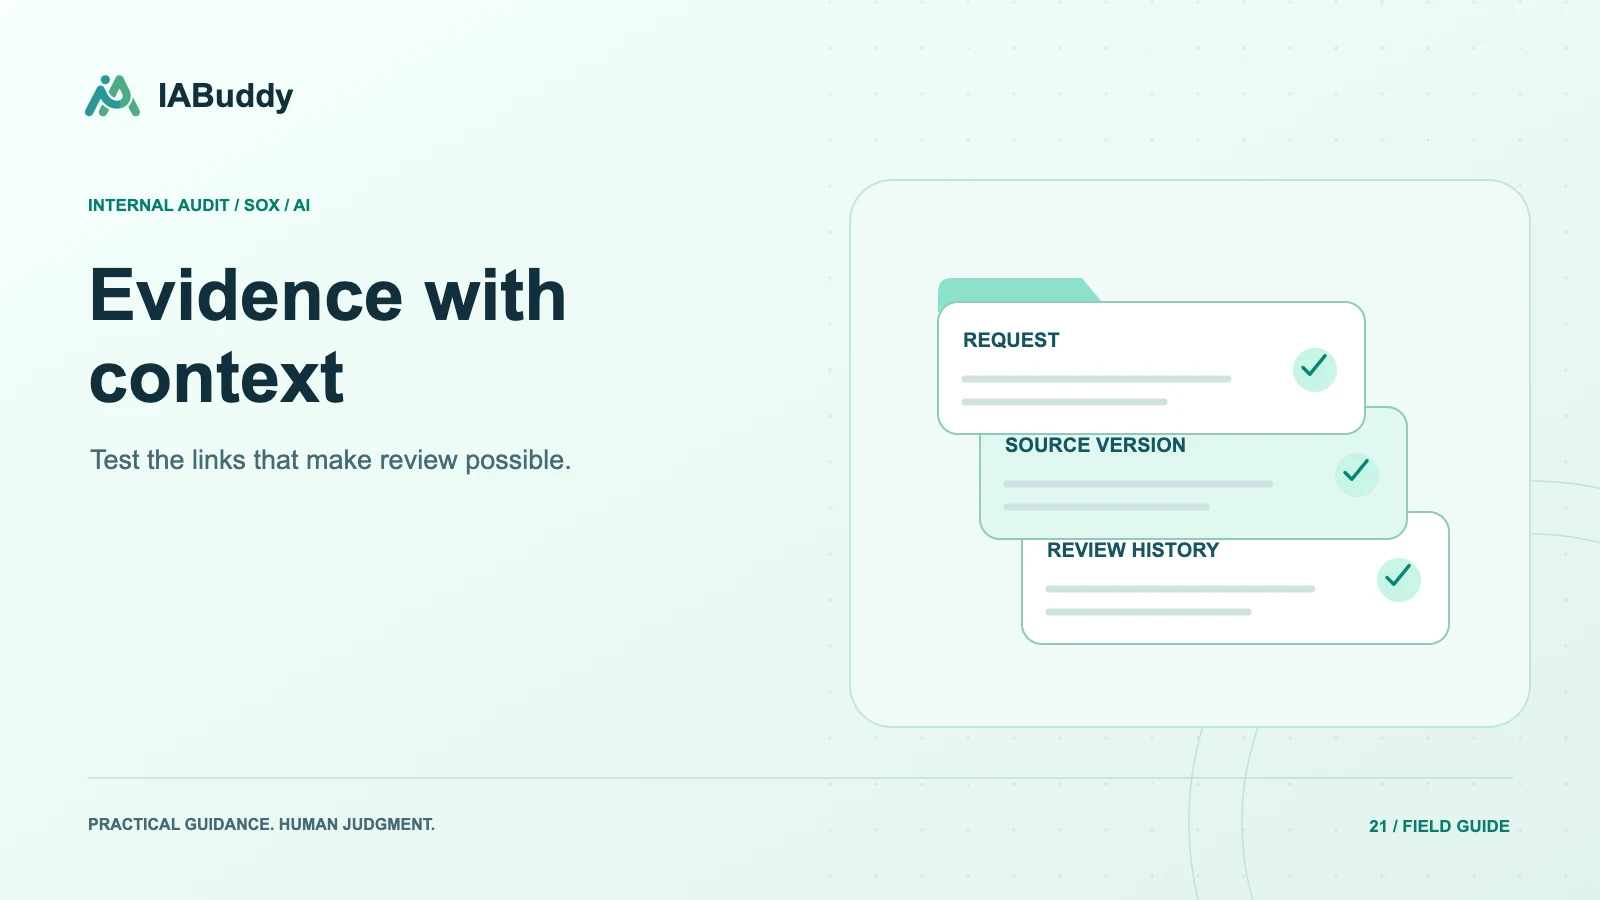
Evaluate evidence management with tests for request linkage, file versions, permissions, source references, review history, exports, and exception follow-up.
Compliance
Compare management assessment with external auditor attestation, understand why SRC status alone does not establish an exemption, and plan the evidence needed.
Compliance
Build a GRC ROI model that separates cash savings from capacity, includes implementation and review costs, and tests assumptions with a measured pilot.
Compliance
Compare IABuddy, Optro, Workiva, and FloQast using workflow scope, demonstrated AI capabilities, implementation needs, evidence review, and written commercial terms.
Compliance
Create clearer PBC requests from controls and samples, define usable evidence, handle incomplete submissions, and preserve review and follow-up context.
Join forward-thinking internal audit teams who are scaling compliance without scaling headcount.
View and analyze control testing performance and outcomes.
Testing Status
Testing by Phase
Testing Conclusion
Control Attestation Status
Controls by significance
Controls mapped to risk
37
AI TESTING COMPLETED
26
CONTROLS READY FOR REVIEW
8
REVIEW IN PROGRESS
3
CONTROLS REVIEWED
6
OPEN ISSUES